How It Works
Compliance That Happens Automatically
No spreadsheets, no manual reviews, no relying on people to remember the rules. It just works in the background.

Recognizes your people
Works with the logins your team already has. Nobody notices a thing, and nobody has to sign in twice.

Knows where they're working from
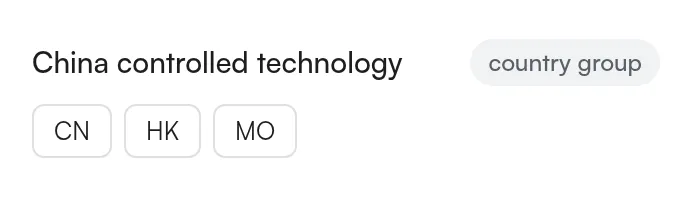
Checks a person's current location against your restricted-country policy. That location comes from the proxy's own IP lookup, or from another source you connect, like an HR feed or a badge system, whichever reported it most recently.

Applies your rules automatically
Company-wide policy, plus tighter rules on your most sensitive projects, applied the same way every time. No manual review needed.

Keeps a record of everything
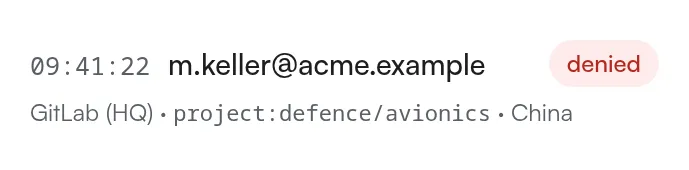
Every access decision is written down, so when compliance or an auditor asks who could see this and when, you have a real answer.
Why Teams Choose It
Real Enforcement That Doesn't Get in Anyone's Way
Built so security and compliance leaders get real enforcement, and engineering teams never have to think about it.
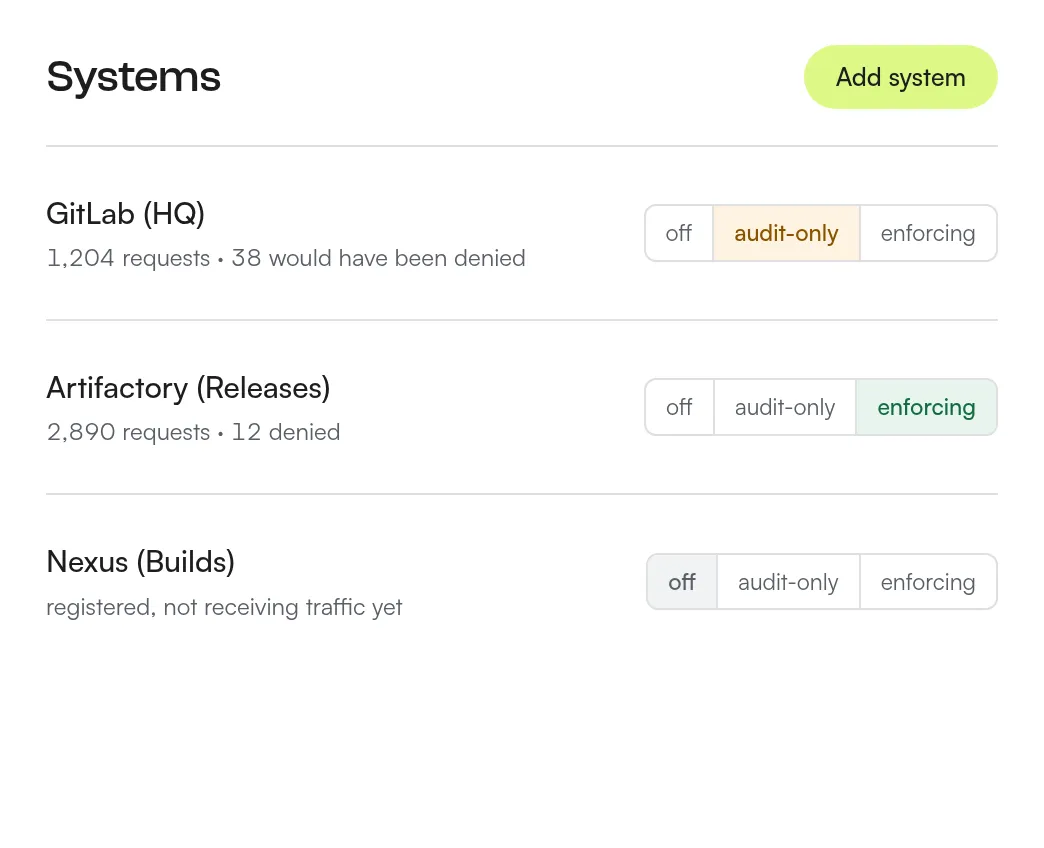
Roll it out with zero risk
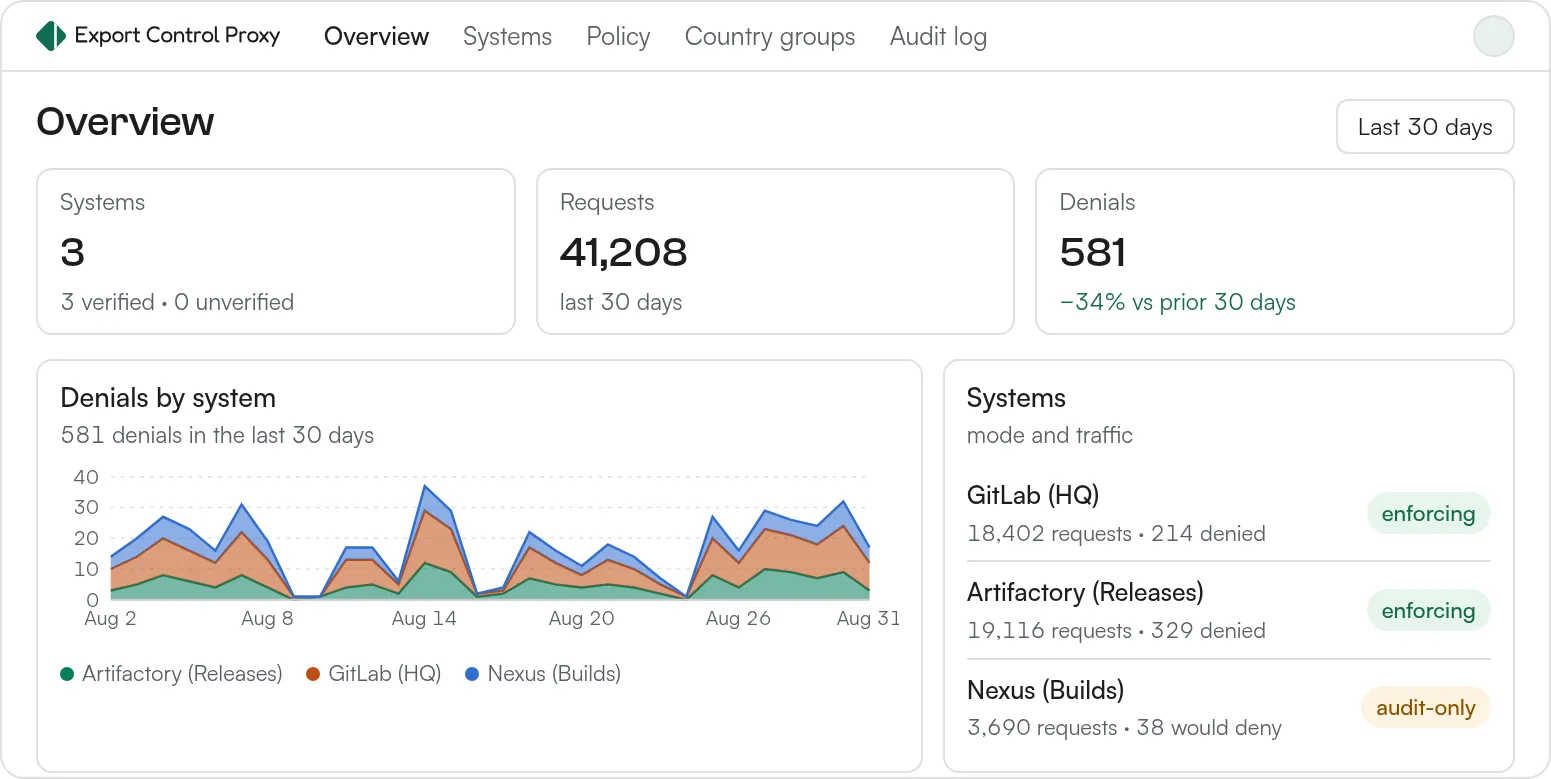
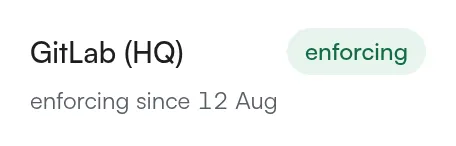
New systems start in audit-only mode, so you see every decision the policy engine would have made before it makes one.
Your team keeps working
When a dependency is unavailable, requests carry on by default. You pick the systems where access should be held instead, and both outcomes are logged as dependency failures rather than policy decisions.
See how it works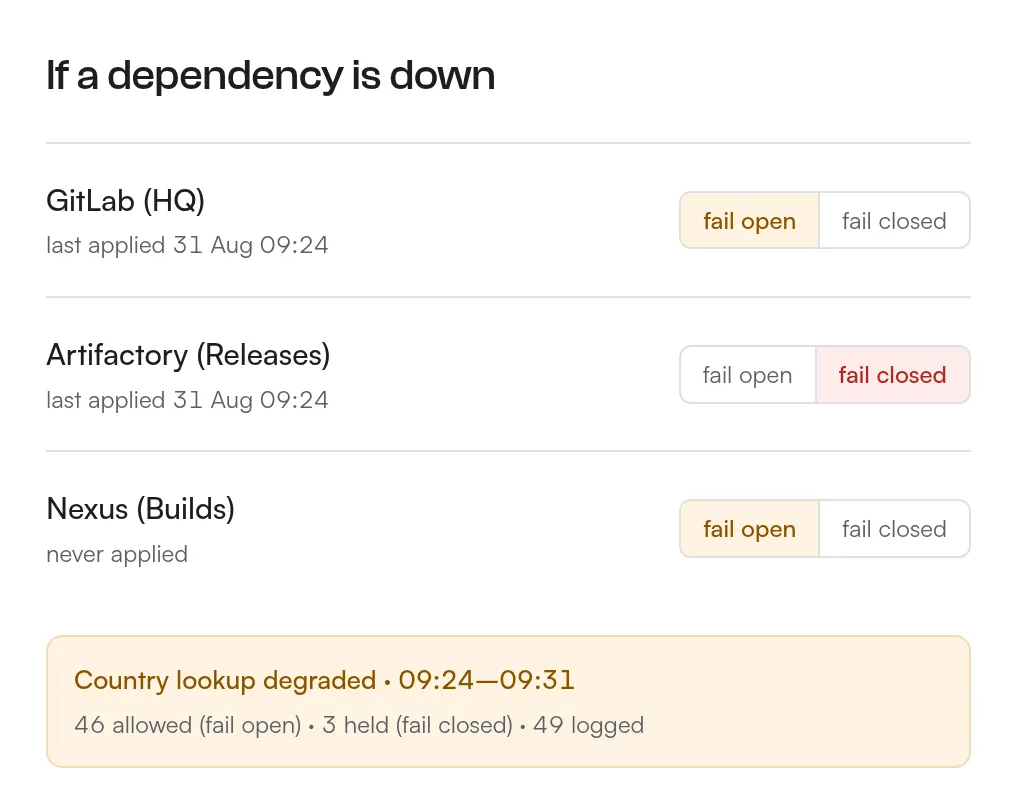
Plans
Choose a Rollout Scope
Every plan runs in your own private cloud, on-prem or in your cloud account, on the Kubernetes you already have, and includes full enforcement, start to finish. Pricing depends on how many systems you're protecting and the support level you need.
Team
For a first rollout covering one or two systems while you get comfortable with audit-only mode.
- Up to 2 protected systems
- Works out of the box with GitLab, Artifactory, and Nexus; see the full list
- Try it in audit-only mode before enforcing anything
- One dashboard for rules, systems, and the audit trail
- Email support
Business
Most commonFor organizations covering most of their internal tools, including command-line git over SSH.
- No limit on protected systems
- Covers command-line git over SSH for GitLab, as well as the web UI
- Takes location from your own HR feed or badge system; most recent record wins
- Priority support during rollout
- Export your audit history anytime
Enterprise
For regulated organizations that need custom coverage and dedicated support.
- Coverage for your own internal or homegrown systems
- Extra-strict controls for your most sensitive projects
- Dedicated support for deployment and rollout
- Single sign-on and custom support agreements
- Source code escrow available for large agreements

Ready to See It in Action?
Tell us which systems you need to protect and we'll show you exactly how it would work for your team.
Contact Sales