Every System, One Engine
One Policy Engine for All Systems
The same identity, location, and policy pipeline covers every protected backend.
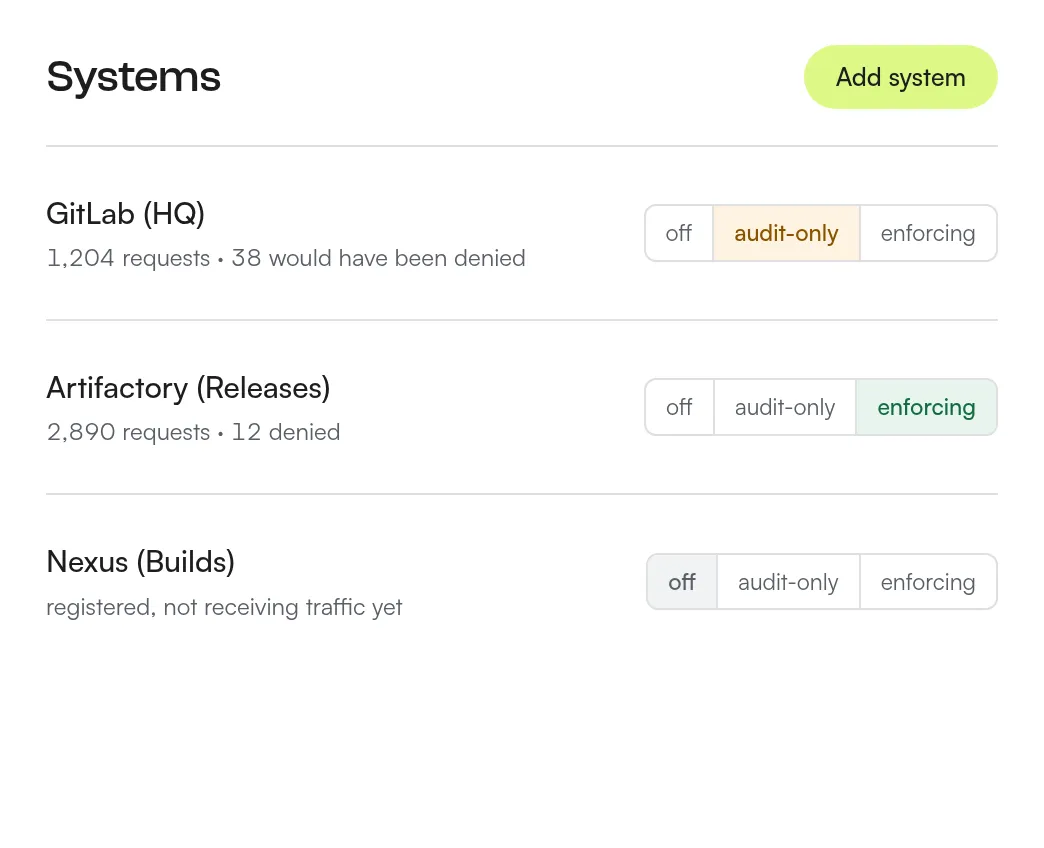
Roll it out with zero risk
New systems start in audit-only mode, so you see every decision the policy engine would have made before it makes one.
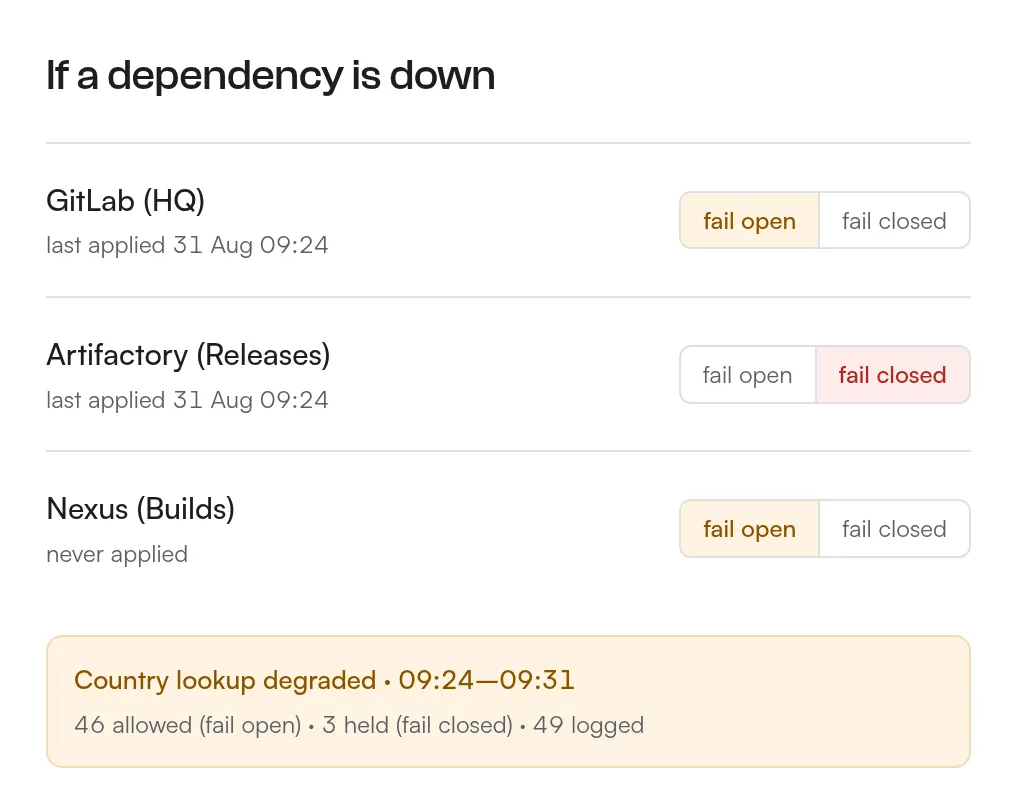
Your team keeps working
When a dependency is unavailable, requests carry on by default. You pick the systems where access should be held instead, and both outcomes are logged as dependency failures rather than policy decisions.
Extensible by Design
Keeps Up as Your Tool Stack Grows
You connect an already-supported system yourself. Anything new gets built for you, not by you.
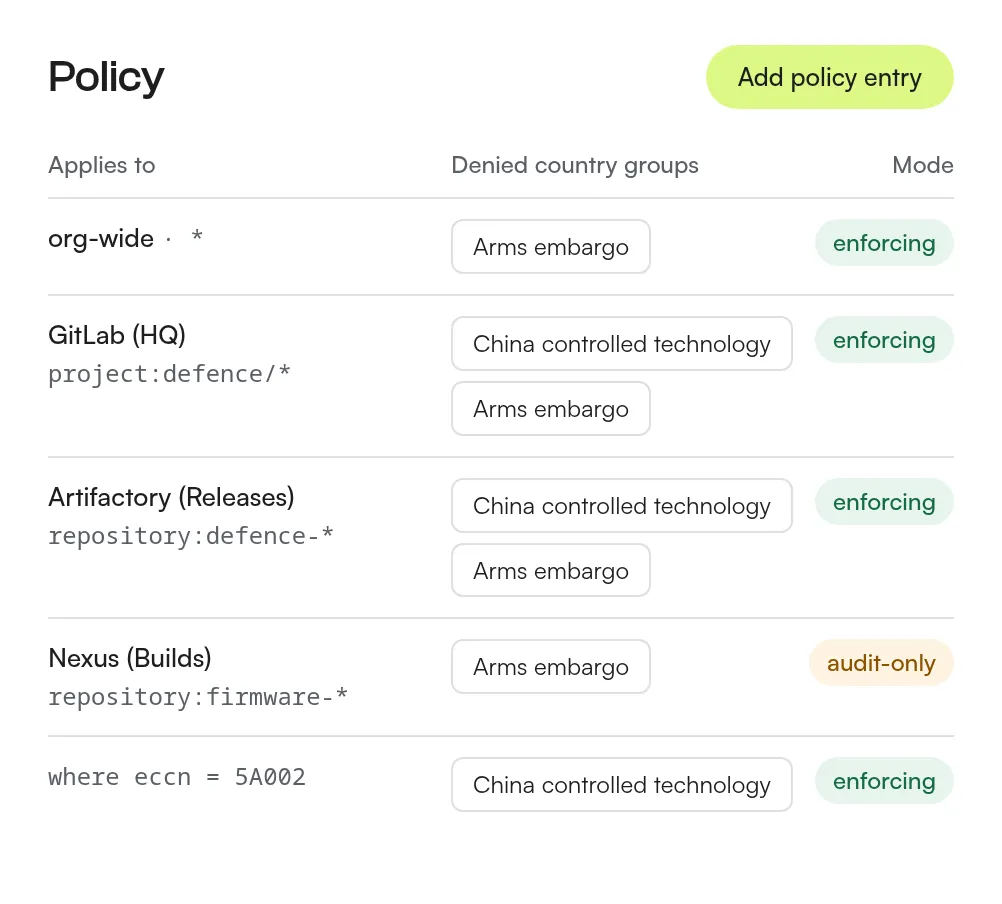
Recognizes who's asking and what they're trying to reach
It works out who's making the request and exactly what they're trying to access, so your rules can be written in plain terms, like a specific project or repository, instead of raw web addresses.

Self-service for supported systems
GitLab, Nexus, and Artifactory are ready to go. Pick the type, add your connection details, and it's live.

We build the rest
Need something we don't support yet? Our team builds that connection as part of onboarding, so your engineers never have to write integration code.
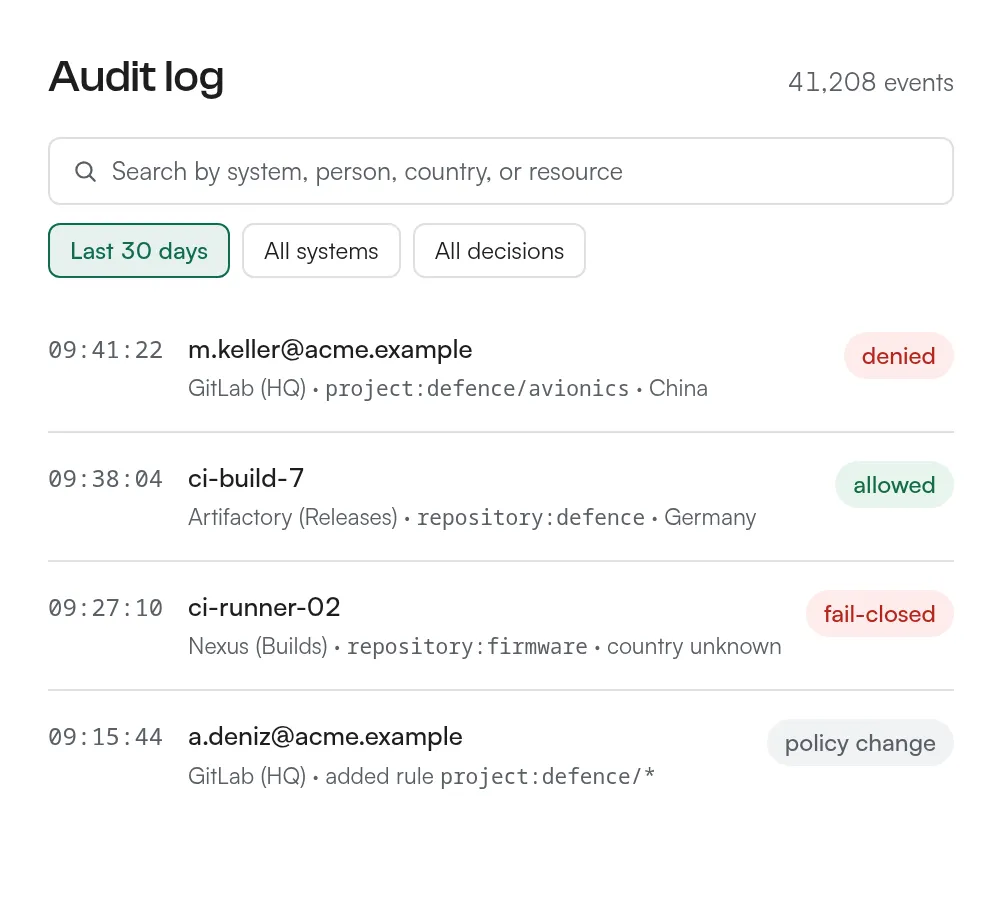
A clear answer for every audit or investigation
Every access decision is recorded and easy to search, along with every change your admins make to the rules. When someone asks what happened, you can show them.
Search by system, person, country, or date, then open any entry to see the full detail behind that decision.
Every change to your setup, like adding a system or updating a rule, is tied to the person who made it.
No technical tools needed. Managing systems, rules, and the audit log all happens in the same place.
Inside the Audit Log
One Log, Every Access Decision
Allow, deny, fail-open, or fail-closed: the audit log is the record security and compliance teams rely on.
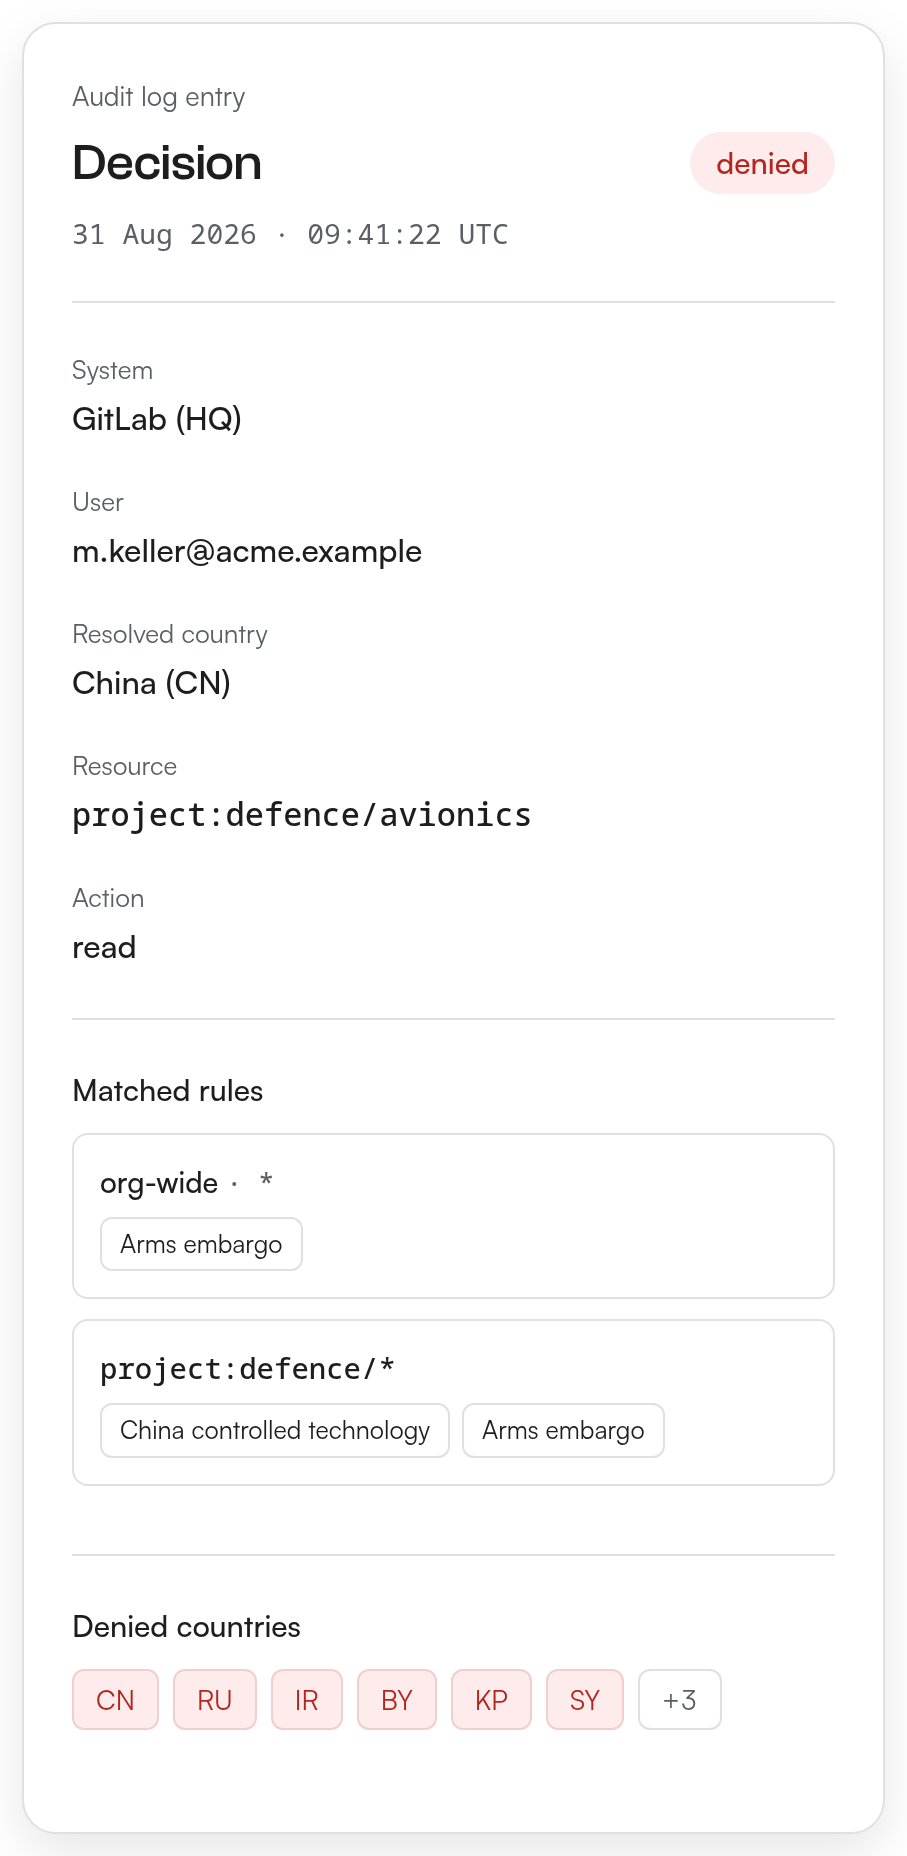
Decision Detail
System, user, resolved country, resource, and every rule that matched, expandable on every row.
Fail-Open or Fail-Closed
Requests allowed or blocked because a dependency was down are logged distinctly from decisions made by policy, whichever way that resource is configured.

Policy Changes
System registration, mode toggles, and rule edits are logged as policy events, attributed to the admin who made them.
Filterable by System
Narrow to one backend, one user, one country, or a time range when investigating a denial.
Audit-Only Traffic
New systems log full decision detail with nothing blocked, so real traffic can be reviewed before enforcement is switched on.
Every Reason for a Denial
A denial isn't traced back to one winning rule. Every rule that matched is listed on the entry, so you see the whole reason someone was blocked, not part of it.

Ready to See It in Action?
Tell us which systems you need to protect and we'll show you exactly how it would work for your team.
Contact Sales